Regulatory Shifts Influencing Cross-Border Domain Transfers adn Portfolio Compliance Frameworks
Bianca Schröder · Oct 3, 2026
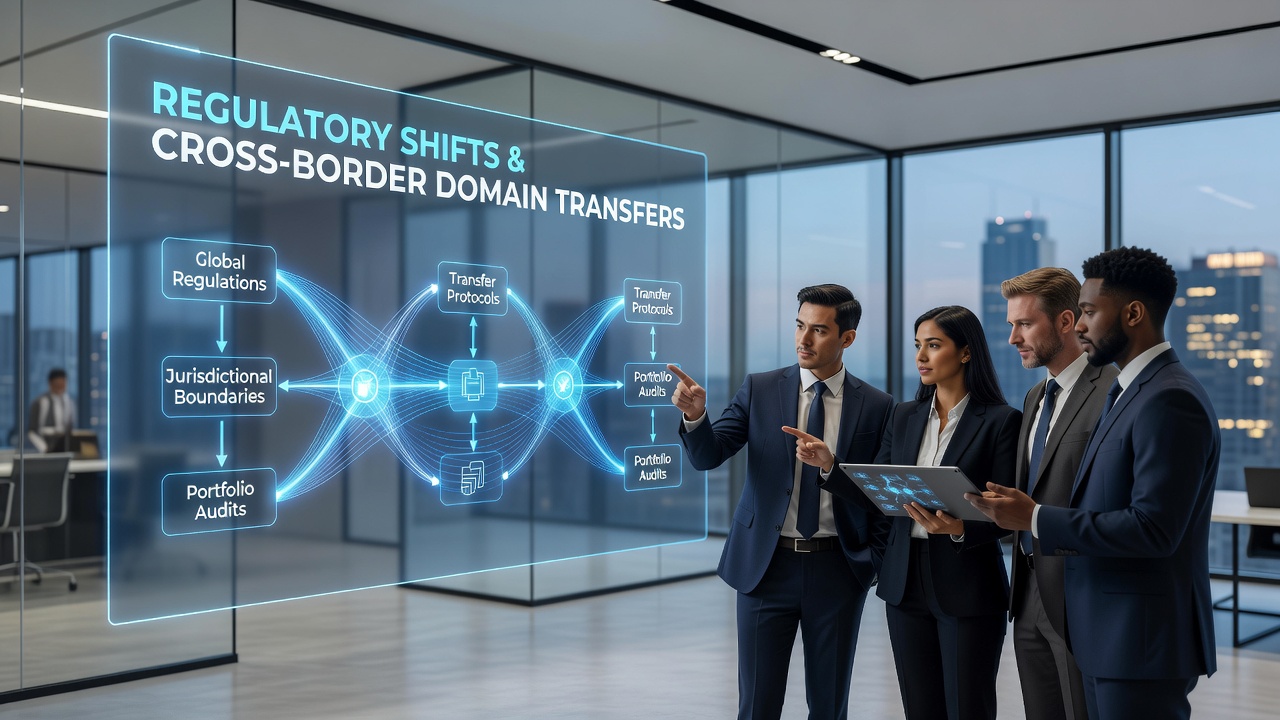
Regulatory Shifts Influencing Cross-Border Domain Transfers adn Portfolio Compliance Frameworks
Domain name transfers across national boundaries now operate under tighter rules that combine ICANN procedures with overlapping data protection statutes from multiple jurisdictions, and observers note these layers create new obligations for portfolio managers who move assets between registrars in different countries. Research from industry reports indicates that transfer volumes have grown steadily since the early 2020s, yet compliance requirements have multiplied because privacy statutes limit the data elements that can travel with each domain record.
ICANN Transfer Policies and Their Global Reach
ICANN maintains the core framework that governs inter-registrar transfers, and its 2019 updates to the Transfer Policy still set the baseline steps registrars must follow while newer regional laws add extra checkpoints. Those who handle large holdings report that the standard 60-day lock after initial registration or prior transfer remains in place, but additional verification steps now apply when the gaining registrar sits outside the original jurisdiction. Data shows that failure to complete these steps can extend processing times by weeks, especially when registrars must reconcile conflicting identification standards.
Data Privacy Laws Reshape Record Transfers
Privacy regulations such as the European Union's General Data Protection Regulation and Canada's Personal Information Protection and Electronic Documents Act restrict how registrant contact data moves during cross-border transfers, and portfolio administrators must therefore obtain explicit consent or rely on legitimate-interest assessments before any WHOIS fields leave one region for another. Similar statutes in Australia and Brazil impose comparable consent requirements, which means a single portfolio spanning multiple continents may need separate compliance pathways for each asset. Figures from regulatory filings reveal that incomplete consent documentation has become one of the leading causes of transfer delays in 2025 and into 2026.
Portfolio Compliance Frameworks Under Pressure
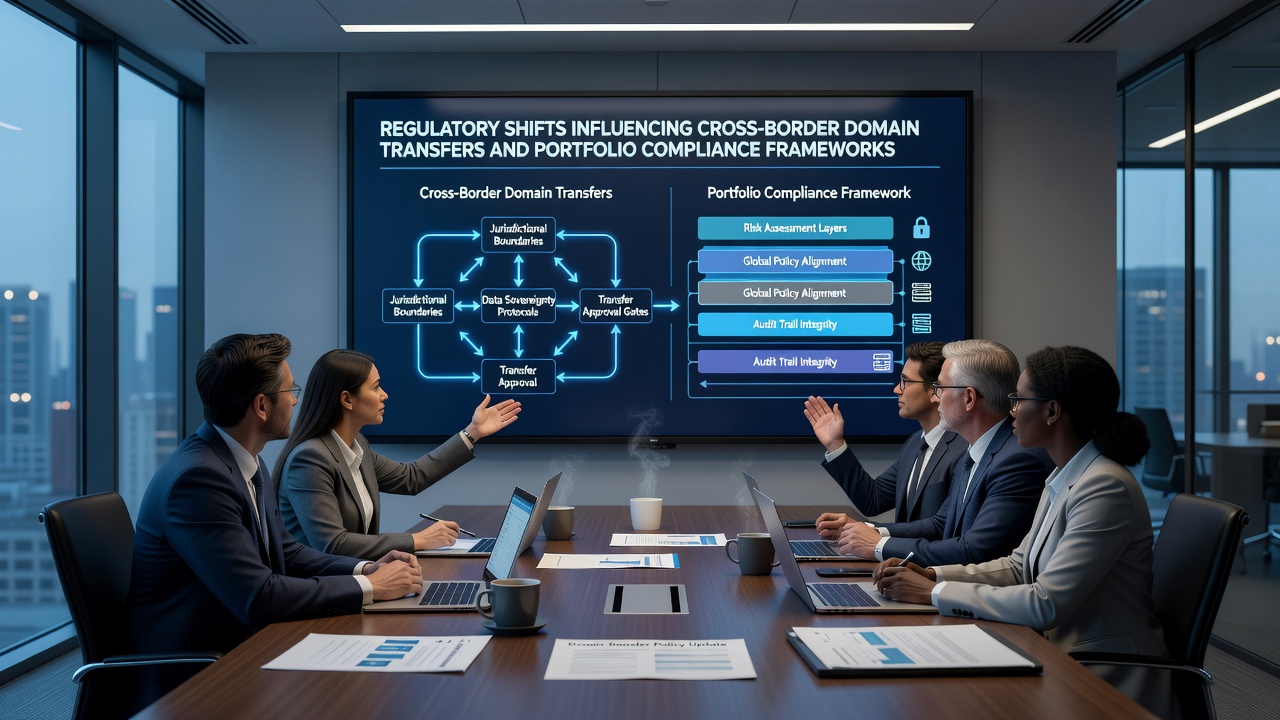
Organizations that maintain thousands of domains across several countries have adopted centralized compliance systems that track each asset's registration history, lock status, and data-handling permissions, and these systems now integrate automated alerts when a transfer request would violate a regional statute. One study of institutional holders found that firms using such platforms reduced rejected transfers by nearly 40 percent compared with manual review processes. Yet the same study noted that smaller holders without dedicated compliance staff continue to experience higher rejection rates because they lack visibility into the shifting rule sets.
Developments Expected in October 2026
October 2026 marks the scheduled start of expanded ICANN contractual compliance audits that will examine how registrars document consent for cross-border data flows, and preliminary guidance issued by ICANN staff indicates that registrars must retain records showing affirmative consent for at least five years after each transfer. Meanwhile, proposed amendments to Japan's Act on the Protection of Personal Information may require additional disclosure language for domains registered under Japanese ccTLDs, creating another layer of documentation for any portfolio that includes .jp names. Observers tracking these timelines report that registrars have already begun updating their transfer forms to capture the new consent fields in advance of the October deadline.
Regional Variations and Their Practical Effects
European registrars must reconcile GDPR with ICANN's minimum data set, whereas registrars in the United States follow a lighter federal approach supplemented by state laws such as the California Consumer Privacy Act, and these differences produce distinct operational workflows for the same domain moving between the two regions. A transfer from a California-based registrar to an EU-based registrar now triggers a review of whether the EU entity can lawfully receive the data under GDPR adequacy decisions, while the reverse direction may require only standard ICANN authorization codes. Portfolio managers who operate in both environments therefore maintain separate checklists that reflect each region's current stance.
Industry Responses and Record-Keeping Practices
Trade associations representing registrars have published model consent templates that incorporate language acceptable under multiple privacy regimes, and several large registrars have adopted these templates to streamline approvals. Research indicates that standardized language reduces back-and-forth between parties and shortens average transfer completion times by several days. At the same time, academic papers examining domain governance highlight that inconsistent enforcement across borders continues to create friction, particularly when a dispute arises over whether consent was properly obtained before data left one jurisdiction.
Conclusion
Cross-border domain transfers now require coordinated navigation of ICANN rules and diverse privacy statutes, and portfolio compliance frameworks have expanded to capture consent records, lock periods, and regional data-flow restrictions. As October 2026 approaches, the scheduled ICANN audits and anticipated changes in Japan illustrate how quickly the landscape continues to evolve, prompting holders to maintain detailed, jurisdiction-specific documentation for every asset. Those who track these developments closely find that early alignment of internal processes with emerging requirements minimizes delays and preserves transfer flexibility across borders.